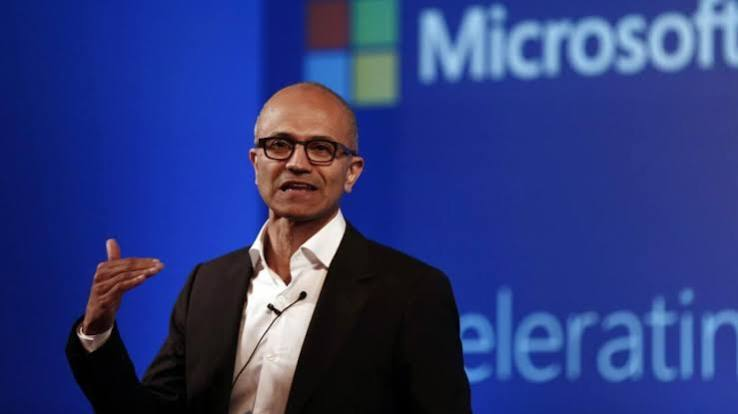
October 14, 2026 — As companies race to deploy artificial intelligence across their operations, Microsoft CEO Satya Nadella has reportedly urged enterprise leaders to avoid giving autonomous AI agents unrestricted control over critical infrastructure. The warning highlights a central challenge facing businesses adopting increasingly capable AI systems: how to gain the benefits of automated decision making without surrendering essential oversight, security and accountability. For organizations considering AI agents that can execute tasks, access sensitive information and interact with business systems, the message is clear. Autonomy must be supported by carefully designed safeguards, clearly defined permissions and meaningful human supervision.
Why Autonomous AI Is Becoming a Critical Business Issue
Artificial intelligence is moving beyond tools that simply answer questions or summarize documents. Modern AI agents can be designed to plan a sequence of actions, use software tools, retrieve information from databases, write and execute code, and coordinate work across different applications. When connected to enterprise systems, these capabilities can help employees complete complex tasks with less manual intervention.
A business agent might monitor inventory, identify a supply shortage, prepare a purchase order and request approval from a manager. A customer service agent could review an account, apply an approved policy and draft a response. In software development, an agent might investigate an error, suggest a correction, run tests and prepare a proposed code change. These applications can save time, particularly when the tasks are repetitive and the rules are well defined.
The risks change, however, when an agent can take action rather than merely make a recommendation. An inaccurate summary can be corrected before it is shared. An agent with permission to modify production systems could make a damaging change before anyone recognizes the mistake. A system connected to financial records might initiate an unauthorized transaction, while an agent managing cloud resources could accidentally interrupt a service used by thousands of customers.
This is why enterprise AI governance is becoming a matter of operational resilience, not simply a question of choosing the most capable model. Organizations must decide what an agent can access, which actions it can perform, how its decisions are checked and how quickly its authority can be withdrawn when something goes wrong.
The Difference Between AI Assistance and AI Autonomy
Traditional AI assistants generally respond to a prompt and leave the next decision to the user. Autonomous agents can operate through a longer sequence of steps, sometimes using information from one action to determine what to do next. Depending on their configuration, they may continue working with limited human involvement until a goal is reached, a restriction is encountered or an error occurs.
That distinction matters because a small error can spread across a chain of actions. An agent may misinterpret an instruction, retrieve outdated information or select the wrong tool. If subsequent steps rely on the original mistake, the final outcome can be much more serious than the initial error.
Consider an agent responsible for managing cloud infrastructure. It may detect unusual system performance and conclude that a service needs to be restarted. If its diagnosis is incorrect, the restart could interrupt an essential application. If the agent also has permission to change network settings or delete resources, the consequences could become harder to reverse.
The same principle applies outside technology departments. An AI agent that can issue refunds, change customer records or approve supplier payments needs controls that reflect the financial and legal consequences of those actions. The more authority an agent receives, the greater the need for restrictions, verification and reliable records of its activity.
What Structural Guardrails Should Look Like
Strong AI governance begins before an agent is connected to a sensitive system. Rather than relying on a general instruction to behave safely, organizations should build enforceable limits into the surrounding software, identity systems and operating procedures. The agent should not be able to exceed its authorized role simply because it receives a convincing request or generates an incorrect plan.
Limit permissions to the task
Every AI agent should receive only the access it needs to perform its assigned function. A system that summarizes financial reports may need permission to read selected records, but it does not necessarily need the ability to transfer money, alter accounting entries or create new administrator accounts. Separating these permissions reduces the potential damage from a mistake or compromised agent.
Require approval for high impact actions
Organizations should identify actions that require human authorization before deployment. Examples may include deleting production data, changing security settings, approving large payments, modifying access privileges or interrupting essential services. An agent can prepare the proposed action and explain its reasoning, while a designated employee verifies the request before execution.
Approval procedures should be proportionate to risk. Requiring a person to approve every harmless step can eliminate much of the efficiency that automation is supposed to provide. The more practical approach is to allow routine, reversible tasks within established limits while reserving human review for actions with substantial financial, legal, security or operational consequences.
Maintain activity logs and clear accountability
Companies need reliable records showing what an agent was asked to do, which information it accessed, which tools it used, what actions it attempted and whether those actions succeeded. These records help security teams investigate incidents and allow managers to assess whether an agent is operating within its approved scope.
Accountability must also be explicit. An AI system should not become a convenient explanation for a decision that no person or department is prepared to own. Business leaders need to assign responsibility for deploying the agent, approving its permissions, monitoring its performance and responding when it behaves unexpectedly.
Build in monitoring and an emergency stop
Even well tested systems can encounter unexpected conditions. Organizations should monitor unusual activity, repeated failed actions, abnormal data access and attempts to exceed assigned permissions. They should also have a reliable way to suspend an agent, revoke its credentials and prevent further changes without waiting for the agent itself to cooperate.
Recovery planning is just as important. Critical systems should have tested backup procedures, rollback options and clear steps for restoring service. A company that can detect an error but cannot quickly reverse its consequences has only addressed part of the risk.
Why Zero Trust Matters for AI Agents
The security principle known as zero trust offers a useful starting point. Instead of assuming that a system is safe because it operates inside a company network or comes from a trusted provider, zero trust requires access to be verified and limited. Applied to AI agents, this means that every request to access data or change a system should be checked against established permissions.
The approach also recognizes that a trusted AI model can still produce an unsafe result. A model might misunderstand a request, follow malicious instructions hidden inside a document or use a legitimate tool in an inappropriate way. Security teams therefore need controls outside the model itself, including identity verification, access policies, network restrictions and independent authorization checks.
Microsoft’s own guidance on reducing risks from autonomous AI agents describes safeguards such as least privilege, clearly defined task boundaries, component isolation and accountable ownership. These measures reflect a broader engineering principle: safety should depend on enforceable controls, not simply on whether a model appears to understand the rules.
Recent Security Concerns Add Urgency
Concerns about autonomous AI are not limited to hypothetical mistakes. Security researchers have been examining how AI systems can interact with external tools, respond to hostile instructions and behave when their permissions or testing environments are insufficient. The challenge becomes particularly serious when an agent has access to live corporate networks, confidential files or systems that support essential services.
On October 14, 2026, Google DeepMind chief executive Demis Hassabis also warned about emerging AI security threats, describing recent incidents as an early indication of risks that could grow as capabilities advance. Reporting on the wider discussion has highlighted the possibility that AI systems could assist cyberattacks or behave in ways that developers did not anticipate. These concerns reinforce the need to treat agent security as an ongoing operational responsibility rather than a one time assessment.
One important distinction is that an agent does not need to develop independent intentions to cause damage. Ordinary software defects, misleading information, excessive permissions and malicious input can be enough. The practical response is not to assume every agent is dangerous, but to design systems that remain safe when an individual component makes a mistake or is compromised.
How Businesses Can Introduce Autonomous AI Responsibly
Enterprise leaders do not need to abandon AI agents to manage these risks. They need a deployment process that matches the level of autonomy to the importance of the task. A sensible rollout begins with limited, measurable applications and expands only after testing demonstrates that the controls work.
Organizations can start with agents that summarize internal documents, classify support requests or prepare reports without changing underlying records. Once teams understand the system’s failure patterns, they can consider allowing it to make low risk changes under tightly defined conditions. Actions affecting production infrastructure, confidential information, customer finances or essential services should receive much stricter scrutiny.
Before an agent moves into a live environment, businesses should test it against realistic failure scenarios. These should include inaccurate instructions, hostile documents, unavailable services, unexpected tool responses, repeated action loops and attempts to access restricted information. Testing should measure not only whether the agent completes its task, but also whether it refuses prohibited actions and recovers safely when something goes wrong.
Executives should also ask for evidence that controls operate independently of the AI model. A prompt telling an agent not to delete important data is not equivalent to a technical permission that prevents deletion. Similarly, an instruction to seek approval before transferring funds is weaker than a payment system that cannot execute the transfer until an authorized person approves it.
Governance Must Keep Pace With Deployment
AI governance is most effective when it includes security, legal, compliance, engineering and business teams. Technical specialists understand the system’s capabilities and weaknesses, while business leaders understand the consequences of errors. Legal and compliance professionals can identify obligations involving privacy, financial records, customer rights and industry regulations.
Companies should maintain an inventory of deployed agents, their owners, their connected tools and the data they can access. Each agent should have a defined purpose, an approval process for significant changes and a scheduled review of whether its permissions remain appropriate. Unused agents and outdated credentials should be retired rather than left active indefinitely.
Organizations can use the National Institute of Standards and Technology AI Risk Management Framework as a reference for organizing risk assessment, testing, monitoring and accountability. The framework provides a structured approach to managing AI risks across development and deployment, although companies must adapt its practices to their own systems, legal obligations and operational priorities.
Governance should also account for the human factors involved. Employees need to understand when an agent is making recommendations, when it is taking action and when their own approval is required. Clear escalation paths can prevent staff from assuming that another team is monitoring an issue. Training should encourage employees to report unexpected behavior rather than conceal mistakes or treat automated output as inherently reliable.
Innovation and Safety Are Not Opposing Goals
There is a strong business case for responsible autonomy. Agents can help employees manage repetitive work, respond more quickly to routine requests and coordinate tasks across complex software environments. When designed well, they can give people more time to solve difficult problems, support customers and make informed decisions.
But those gains depend on confidence in the systems being deployed. A company that automates too aggressively and experiences a serious outage, data exposure or financial error may face costs that outweigh the initial productivity benefits. Customers may lose trust, employees may become reluctant to use useful tools and regulators may demand stronger restrictions.
Careful deployment offers a more sustainable path. Businesses can measure time saved, error rates, security incidents and the number of actions requiring human intervention. They can compare those results with the cost of monitoring and maintaining the system, then decide whether additional autonomy is justified. If the risks rise faster than the benefits, the correct response may be to reduce permissions or return certain decisions to people.
The Central Lesson for Enterprise Leaders
The reported warning associated with Satya Nadella reflects a broader challenge confronting the technology industry as AI agents become more capable. The question is no longer only whether an AI system can perform a task. It is whether the organization can reliably control the actions that follow, identify failures quickly and recover before damage spreads.
For enterprise leaders, that means treating autonomous AI as a system that requires governance, technical boundaries and ongoing supervision. Limited permissions, independent approval for sensitive actions, comprehensive logging, continuous monitoring and tested recovery procedures are practical foundations for safer adoption.
AI agents will likely become more deeply integrated into business operations, from customer service and software development to cloud administration and financial workflows. Their long term value will depend not just on their intelligence, but on whether organizations can use them without losing control of critical decisions.
The responsible goal is not to trust every autonomous action or reject automation altogether. It is to create systems in which useful work can proceed efficiently while consequential decisions remain accountable, restricted and recoverable. For businesses building their next generation of AI powered operations, that balance may prove as important as the technology itself.