A reported September 16, 2026 framework from the International Court of Justice on cross border corporate data flows and citizen privacy could have major implications for companies operating across national borders. However, our review of publicly available International Court of Justice material does not substantiate the claim that the ICJ issued a new advisory framework specifically governing transboundary data privacy on that date. The distinction matters because international data protection is currently shaped by national legislation, regional privacy regimes, international agreements and decisions from several different courts and institutions.
What the International Court of Justice Has Actually Been Addressing
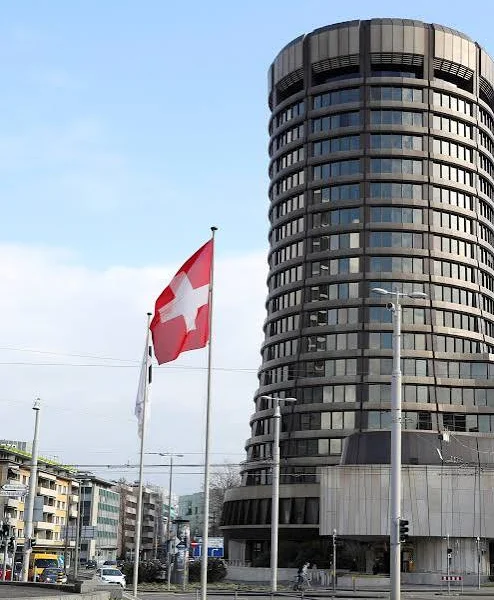
The International Court of Justice, based in The Hague, is the principal judicial organ of the United Nations. Its work includes disputes between states and advisory opinions requested by authorized United Nations bodies and agencies. It does not operate as a general global privacy regulator for private companies.
Recent ICJ advisory proceedings have dealt with major questions of international law, including state obligations relating to climate change and environmental harm. The Court’s published material concerning the climate advisory proceedings shows that the questions before it were centered on state obligations under international law, environmental protection, human rights and the consequences of climate related harm. There is no indication in those proceedings of a new global corporate data privacy regime.
That distinction is especially relevant when evaluating reports that describe the ICJ as having issued updated rules for multinational companies. An advisory opinion from an international court and a binding regulatory framework imposed directly on private businesses are not interchangeable legal instruments.
Why Cross Border Data Privacy Has Become a Global Legal Issue
Even without a new ICJ privacy framework, the underlying issue described in the reported announcement is very real. Companies routinely move personal information between countries when customers purchase products online, employees use cloud software, banks process international payments or businesses outsource technology services.
A single customer record might be collected in one country, processed by a cloud provider in another and backed up on servers located somewhere else. The person whose information is being processed may have little visibility into those transfers.
For businesses, the legal challenge is therefore not simply deciding whether data can cross a border. Companies must determine what personal information they hold, where it travels, who can access it, what safeguards apply and which laws govern each stage of processing.
Europe Remains a Major Reference Point for Privacy Rules
The European Union’s General Data Protection Regulation remains one of the world’s most influential privacy regimes. Its rules apply to organizations processing personal data in circumstances covered by European law, including certain organizations outside the European Union that offer services to people in the region or monitor their behavior.
The GDPR also contains specific requirements concerning transfers of personal data to countries outside the European Economic Area. Companies may need an adequacy decision or an appropriate transfer mechanism, depending on the circumstances.
The European Commission provides detailed guidance on international transfers of personal data, illustrating how cross border privacy governance is currently being developed through regional law and international arrangements rather than through one universal ICJ rule.
Privacy Is Becoming a Supply Chain Responsibility
The practical consequences extend well beyond a company’s own servers. Modern organizations often depend on cloud providers, payment processors, analytics companies, customer relationship platforms, human resources systems and external software vendors.
That means privacy compliance can depend on contracts and technical controls throughout a company’s technology supply chain. A business may collect information responsibly but still face regulatory exposure if a service provider transfers or processes that information without an appropriate legal basis or security arrangement.
For this reason, cross border privacy assessments increasingly involve vendor due diligence, data mapping, encryption, access controls, retention policies and documented transfer mechanisms.
International Law Still Has a Role
The absence of a verified ICJ data privacy framework does not mean international law has no relevance to cross border information issues. International law can influence how states exercise jurisdiction, how governments cooperate and how treaties interact with domestic legal systems.
The ICJ’s broader jurisprudence also demonstrates that international law can address conduct producing effects beyond national territory. In its climate related proceedings, for example, submissions to the Court examined the legal significance of transboundary harm and the responsibilities of states when activities produce effects beyond their borders.
Those principles should not automatically be presented as a global data privacy rule. Environmental harm, state responsibility and corporate personal data processing involve different bodies of law. Treating them as identical would risk giving businesses and consumers an inaccurate picture of their legal rights.
What Companies Should Be Doing Now
Organizations that transfer personal information internationally do not need to wait for a hypothetical universal privacy framework before reviewing their practices. Existing privacy laws already create substantial responsibilities in many jurisdictions.
A practical compliance review should begin with a clear map of personal data. Companies should identify what information they collect, why they collect it, where it is stored, which vendors receive it and which countries may be involved in processing.
Organizations should also review their international transfer mechanisms and contractual arrangements with service providers. Technical protections such as encryption and strong access controls can reduce exposure, while clear retention policies can limit the amount of personal information held unnecessarily.
For multinational businesses, legal teams should also track changes in each relevant jurisdiction rather than assuming that compliance with one privacy law automatically satisfies another country’s requirements.
Consumers Face a Different Challenge
For individuals, cross border data processing can be difficult to see. A person may provide a name, email address or payment detail to a familiar company without realizing that several technology providers may process that information behind the scenes.
Privacy notices can provide useful information, although their length and legal language can make them difficult for ordinary users to interpret. Consumers can pay particular attention to information about international transfers, third party processors, retention periods and available rights.
Where privacy law provides access, correction, deletion or objection rights, individuals may also have mechanisms for asking organizations how their information is being used. The precise rights vary according to the jurisdiction and circumstances.
Artificial Intelligence Adds Another Layer of Complexity
The expansion of artificial intelligence is making international data governance even more complicated. AI systems may rely on large datasets, cloud infrastructure and service providers located in several countries. Personal information can therefore move through multiple technical environments during development or deployment.
This creates questions about data minimization, lawful processing, automated decision making, security and accountability. Businesses using external AI services may also need to determine whether customer or employee information is being used for model training, monitoring or other secondary purposes.
The legal environment is changing quickly, but the fundamental compliance questions remain familiar. Organizations need to know what data they have, why they are processing it, where it goes and who is responsible for protecting it.
Why the Reported ICJ Announcement Deserves Careful Verification
International legal developments can have significant consequences for businesses, governments and individuals, which makes precise attribution essential. Describing the ICJ as having issued a universal privacy standard could lead companies to believe that a new binding global rule has replaced existing national and regional requirements.
The publicly available ICJ material reviewed for this report does not establish that such a data privacy advisory opinion was issued on September 16, 2026. The Court’s documented advisory work includes major questions involving international environmental law and state obligations, but those proceedings should not be presented as a new corporate privacy code.
The International Court of Justice’s official case and advisory opinion records remain the appropriate place to verify a purported Court ruling, particularly when a report describes a major new international legal framework.
The Bigger Story Is Still About Global Data Governance
Although the reported ICJ framework cannot presently be confirmed from the Court’s published material, the underlying subject is increasingly important. Cross border data flows are now woven into ordinary commerce, cloud computing, financial services, healthcare, employment and artificial intelligence.
The challenge for lawmakers is finding a workable balance between international digital commerce and meaningful privacy protection. The challenge for companies is complying with a growing collection of legal requirements without creating unnecessary barriers to legitimate data processing.
For consumers, the central issue is trust. People increasingly expect organizations to know where their information goes and to protect it when it crosses a national boundary. That expectation is unlikely to disappear simply because privacy regulation remains divided among different legal systems.
For now, the strongest conclusion is therefore a measured one. There is no verified basis in the ICJ material reviewed here for treating September 16, 2026 as the date of a new universal ICJ framework for corporate cross border data transfers. What is clear is that international data governance continues to develop rapidly, and companies operating across borders will need to follow multiple legal regimes while maintaining strong technical and organizational safeguards for the people whose information they handle.